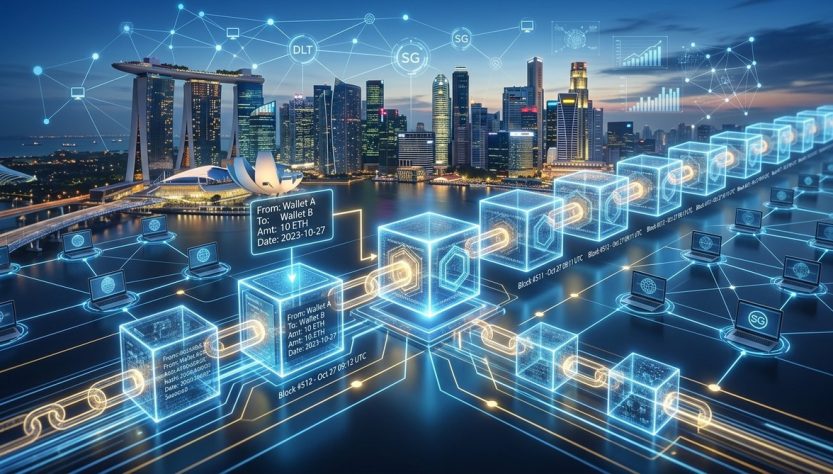
Picture a shipping container full of electronics leaving the Port of Singapore. It gets loaded onto a vessel, clears customs, arrives in Jakarta, and moves through three warehouses before reaching a store. At every step, someone records a handoff. But what if those records could be altered after the fact? What if a dishonest warehouse manager changed the timestamp to hide a delay? In a traditional database, that is possible. On a blockchain, it is not. Every single transaction, from the moment it is submitted to the moment it is confirmed, leaves a permanent, visible, and unchangeable mark. That is the power of the blockchain audit trail.
A blockchain audit trail is not a feature you can turn off. It is the direct result of how distributed ledgers work. Every transaction is cryptographically linked to the one before it, copied across dozens or thousands of nodes, and permanently sealed by a consensus mechanism. For compliance officers and business leaders, this means tamper evidence is built in. You do not need to trust a single auditor or database administrator. The code enforces the record.
The Architecture Behind an Indelible Record
To understand why a blockchain audit trail is permanent, you need to look at the three layers that make it possible. These layers work together to ensure that once data lands on the chain, it cannot be erased or quietly changed.
1. Cryptographic linking (the chain itself).
Every block contains the hash of the previous block. A hash is a unique digital fingerprint. If someone tries to alter a transaction inside block number 400, the hash of that block changes. Since block 401 contains the old hash, it no longer matches. The mismatch propagates through every subsequent block. The network detects the break instantly.
2. Distribution across nodes.
A single copy of the ledger does not exist. Instead, hundreds or thousands of independent nodes each hold a full copy. If one node tries to show a different version of history, the network compares it against the majority. The minority copy is rejected. This is not a theoretical safeguard. It is the daily reality of public and permissioned blockchains.
3. Consensus finality.
Before a transaction is added to the chain, a consensus mechanism (proof of work, proof of stake, or a Byzantine fault tolerance algorithm) must agree that it is valid. Once that agreement is reached and the block is added, reversing it requires recreating all the work of that consensus for every block that came after. On a mature network like Bitcoin or Ethereum, that cost is astronomically high.
How the Audit Trail Works in Practice
Let us walk through a real scenario. Imagine you are a compliance officer at a Singapore-based trading firm. You receive a shipment of coffee beans from Vietnam. The bill of lading, the inspection certificate, and the payment confirmation are all recorded on a private blockchain used by your consortium.
Here is what happens step by step:
- Your system creates a transaction that includes the shipment ID, the hash of the PDF certificate, the timestamp, and your digital signature.
- The transaction is broadcast to the network. Validating nodes check your signature and confirm that you have permission to write.
- The validators group your transaction with several others into a candidate block.
- The consensus protocol runs. In a Hyperledger Fabric network, this might be a simple majority vote among known validators.
- Once consensus is reached, the block is appended to the chain. Every node updates its local copy.
- The new block contains the hash of the previous block, sealing the entire history up to that moment.
If a bad actor later tries to change the inspection certificate hash inside that block, they would need to alter the block, recalculate its hash, alter every subsequent block, and convince more than half the network to accept the rewritten history. On a well-governed enterprise chain with 20 validating nodes, that is nearly impossible. On a public chain with thousands of nodes, it is effectively impossible.
What Makes a Blockchain Audit Trail Different from a Database Log
Many enterprise systems already keep audit logs. A database can record who changed what and when. But those logs are stored on a server that the company controls. Someone with root access can edit the log file. Even the most secure database has a single point of failure: the admin account.
A blockchain audit trail removes that single point. Here is a comparison:
| Feature | Traditional Database Log | Blockchain Audit Trail |
|---|---|---|
| Storage location | Central server or cluster | Distributed across all nodes |
| Editability | Possible with admin rights | Impossible without network majority |
| Timestamp integrity | Relies on server clock | Relies on block height and consensus |
| Transparency | Limited to internal team | Visible to all permissioned participants |
| Recovery after tampering | Restore from backup | Chain rejects invalid history |
For a compliance officer reporting to the Monetary Authority of Singapore, this difference matters. Regulators increasingly expect firms to demonstrate that their records have not been tampered with. A blockchain audit trail provides cryptographic proof, not just an assertion.
Common Misunderstandings About Blockchain Immutability
Even experienced professionals sometimes get this wrong. Here are a few myths that still circulate.
-
Myth: “Blockchain data can be edited if you have the private key.”
Your private key lets you sign new transactions. It does not let you rewrite history. Once a transaction is included in a block, no key can change it. -
Myth: “A 51% attack lets you rewrite the entire chain.”
A 51% attack gives an attacker control over the consensus process for future blocks. It does not let them alter past blocks without redoing all the work. On large networks, rewriting even a few hours of history would cost tens of millions of dollars. -
Myth: “Private blockchains are not really immutable because the network is small.”
A private blockchain with 10 nodes is still more tamper resistant than a shared spreadsheet. Each node holds a full copy. An attacker would need to compromise at least six of those ten nodes simultaneously. That is harder than editing a single database.
“The audit trail is not an add on. It is the natural output of the system’s design. If you understand how blocks link together, you understand why tampering is visible.” — Lead engineer, DLT Singapore
For a deeper look at how blocks are constructed, read our guide on what exactly is inside a blockchain block.
How to Verify an Audit Trail on Chain
You do not need to be a developer to check a blockchain audit trail. Most blockchains offer block explorers that display every transaction. Here is a simple process you can use as a compliance professional.
- Find the transaction ID. Every transaction has a unique hash. This is usually provided by the system that submitted the transaction.
- Look up the block number. Paste the transaction hash into a block explorer. The explorer shows which block contains it.
- Check the previous block hash. Every block header includes the hash of the block before it. You can trace this backward all the way to the genesis block.
- Confirm the block height. The block number tells you where this transaction sits in the chain. A higher block number means more confirmations have been built on top.
- Verify the timestamp. Block timestamps are not precise to the millisecond, but they are anchored to the chain. If someone claims a transaction happened on a different date, the block height exposes the lie.
This verification process works for both public chains like Ethereum and permissioned chains like Hyperledger Fabric. The only difference is who can access the block explorer. In a private network, access is limited to authorized participants.
Why Enterprise Teams Are Adopting Blockchain for Compliance
In 2026, regulatory pressure around data integrity is higher than ever. The Monetary Authority of Singapore requires financial institutions to maintain accurate and tamper evident records. Traditional databases struggle to prove the absence of tampering. They can only prove that no tampering was detected.
A blockchain audit trail turns that around. It provides a mathematical guarantee that the data has not been changed since it was recorded. For supply chain finance, trade finance, and digital asset custody, this is a game changer.
Consider a bank that uses a private blockchain to record letters of credit. When an auditor arrives, they do not need to trust the bank’s database administrator. They can pull the chain data directly, verify the hashes, and confirm that every amendment was recorded in order. The audit becomes faster, cheaper, and more reliable.
If your organization is evaluating whether to move to a distributed ledger, start by reading our comparison of public vs private blockchains. That decision will shape your audit trail design.
The Limits of Blockchain Audit Trails
No system is perfect. Blockchain audit trails have a few limitations that every compliance officer should know.
- Off-chain data is not protected. If you store a PDF outside the chain and only put its hash on the ledger, the PDF itself can be altered. The chain will tell you that the hash no longer matches, but it cannot prevent the change.
- Timestamps are approximate. Block times come from the validator’s clock, which can be off by a few seconds or minutes. For most compliance use cases, this is acceptable. For millisecond precision, you need a different approach.
- Permissioned chains require trust in the validators. If your consortium controls all the nodes, a colluding majority could theoretically rewrite history. The risk is lower than a single database, but it is not zero.
For a full discussion of these edge cases, see our article is blockchain really immutable.
Practical Steps to Implement a Blockchain Audit Trail
If you are ready to build or join a blockchain network for compliance purposes, follow these steps.
- Choose the right consensus model. For enterprise use, proof of stake or a permissioned Byzantine fault tolerance algorithm often works better than proof of work. They use less energy and settle transactions faster.
- Define who can read the trail. In a private network, you can restrict read access to regulators, auditors, and partner organizations. This balances transparency with data privacy.
- Automate verification. Build a dashboard that periodically checks the chain’s integrity. It should alert you if any block hash does not match the expected value.
- Integrate with existing systems. Your ERP or trade finance platform should automatically submit transaction hashes to the chain. Manual entry defeats the purpose.
Our team at DLT Singapore has helped several enterprises set up compliant blockchain audit trails. If you are curious about the technical roadmap, check out our guide on integrating legacy systems with enterprise blockchain.
The Role of Smart Contracts in Automating Audit Trails
Smart contracts take the audit trail one step further. They encode business rules directly into the chain. When a condition is met, the contract automatically executes and records the result. That result becomes part of the permanent trail.
For example, a smart contract for a trade finance agreement might say: “Release payment to the supplier when the shipping container’s GPS tracker shows arrival at the port.” The GPS data is fed into the contract via an oracle. The contract checks the condition, releases the funds, and writes the entire event to the chain. No human intervention, no dispute over whether the condition was met.
This automation is especially valuable in Southeast Asia, where cross border trade involves multiple parties, languages, and legal systems. A smart contract audit trail removes ambiguity. Every party sees the same immutable record.
To learn more, read our explanation of how smart contracts actually execute on Ethereum virtual machine.
Why Singapore Is the Natural Home for Blockchain Audit Trails
Singapore’s regulatory environment actively encourages the use of distributed ledger technology for compliance. The Monetary Authority of Singapore has issued guidelines that recognize blockchain records as admissible evidence. The city state’s Project Ubin and subsequent initiatives have proven that blockchain can handle high volume financial transactions.
For a business professional based in Singapore, adopting a blockchain audit trail aligns with both regulatory expectations and competitive advantage. Your partners in Jakarta, Bangkok, and Kuala Lumpur can verify your records without needing to trust your internal systems. The chain provides a shared source of truth.
If you are exploring this path, you might find value in our article on how Singapore banks are actually using blockchain technology.
Your Next Move in Building a Permanent Audit Trail
A blockchain audit trail is not a magic wand. It is a tool. It gives you something that traditional databases cannot: cryptographic proof that your records have not been altered. For compliance officers facing regulatory scrutiny, for supply chain managers tracking goods across borders, and for technical researchers building the next generation of financial infrastructure, that proof is invaluable.
Start small. Pick one process, like a letter of credit or a certificate of origin, and record its hash on a test network. Verify the trail yourself. See how the blocks link together. Once you feel the certainty that comes from a tamper evident system, you will understand why every blockchain transaction creates a permanent audit trail.
If you want to go deeper, our team publishes regular guides on enterprise DLT. Read our breakdown of why do blockchains need consensus mechanisms to understand the final piece of the puzzle. Then reach out. We would love to help you build an audit trail that regulators trust and your team can rely on.